Operational Technology (OT), the hardware and software that runs physical equipment such as building management systems, industrial control systems, medical devices, CCTV, access control, and manufacturing equipment, is often invisible to a business’s IT strategy until something goes wrong. Unlike IT, which most SMBs monitor and back up as a matter of course, OT is frequently unmanaged, undocumented, and unprotected. This article sets out a practical approach to mapping your OT environment, understanding where its data lives, and building backup and security plans around it.
What Is OT, and Why Is It Different From IT?
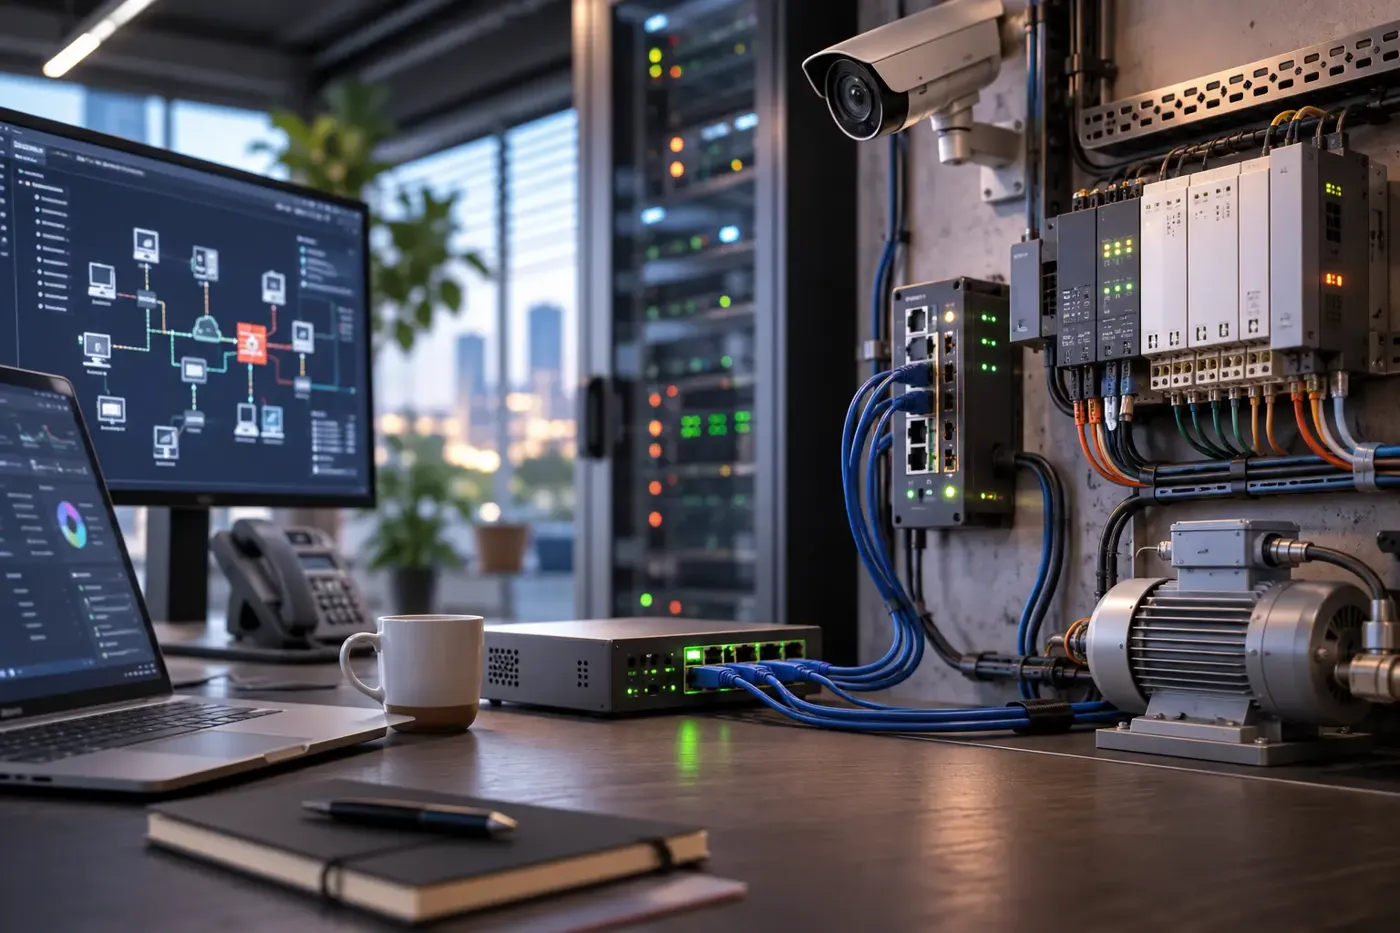
IT (Information Technology) manages data: email, files, applications, and the networks that move them. OT (Operational Technology) manages physical processes: it opens doors, controls temperature, monitors patients, runs production lines, and records footage. Common examples in an SMB environment include:
- Building management systems (HVAC, lighting, access control)
- CCTV and physical security systems
- Industrial control systems and PLCs (programmable logic controllers)
- SCADA systems monitoring plant or utility processes
- Medical devices and diagnostic equipment
- Point of sale and warehouse automation hardware
- Environmental sensors and monitoring equipment
The key difference for security purposes: IT systems are usually patched, backed up, and centrally managed by an IT team. OT systems are usually installed by a specialist vendor, run on legacy operating systems that can’t be patched without voiding a warranty or breaking compatibility, and are managed (if at all) by whoever installed them, not by IT. That gap is exactly where risk accumulates.
Why OT Security Has Become an IT Problem
Historically, OT and IT ran on separate networks and nobody worried about the crossover. That’s no longer true. Most OT systems today are IP connected for remote monitoring, vendor support, or reporting, which means they sit on the same network as your business data, whether anyone planned it that way or not. This convergence creates two specific risks:
- OT as an entry point. A vulnerable, unpatched OT device (an old CCTV NVR, a building controller with a default password) is often the easiest way into a network, not the servers protected by modern cyber security stacks.
- OT as an uninsured, unrecoverable asset. If ransomware hits, IT can usually be restored from backup within hours. If an industrial controller’s configuration is wiped and nobody has a backup of it, or the only person who knew how to reconfigure it left the business two years ago, the outage can run into days or weeks.
For Australian businesses working toward Essential Eight, ISO27001, or SMB1001 compliance, OT is increasingly in scope. An asset inventory and backup strategy that only covers servers and laptops leaves a genuine gap in both your security posture and your audit evidence.
Step 1: Map What OT You Actually Have
You can’t protect or back up what you haven’t identified. Most businesses are surprised by what turns up in this exercise. A proper OT map should record, for every device:
- What it is and what it controls
- Who installed it and who supports it (internal team or third party vendor)
- Whether it’s network connected, and if so, on which network or VLAN
- Whether it has a management interface, and who holds the login
- Its current firmware or software version and patch status
- Its physical location
The most reliable way to build this list isn’t a spreadsheet exercise done from memory, it’s a physical walkthrough combined with a network scan. Network discovery tools will surface connected devices that nobody remembers installing; the walkthrough catches devices that aren’t network connected at all but still need to be accounted for in a disaster recovery plan.
Step 2: Know Where the Data Actually Lives
Once devices are mapped, the next question is where their data goes. OT data storage tends to fall into one of four patterns, and each carries different risk:
- On device storage. Configuration and logs live only on the device itself (common with CCTV NVRs, older PLCs). If the device fails, the data is gone unless it’s been backed up separately.
- On premises historian or server. Industrial and building management systems often log to a local server or ‘historian’ database. This is backed up if it’s inside your existing IT backup scope, and frequently isn’t, because it was set up by the OT vendor, not IT.
- Vendor hosted cloud platform. Increasingly common for building management and medical devices. Convenient, but it means your data’s availability depends entirely on a third party’s uptime, backup practices, and continued business existence.
- Hybrid. Local caching with cloud sync, which is generally the most resilient pattern but needs to be confirmed, not assumed.
The practical exercise here is to trace every OT system on your map back to where its data is actually written and stored, and confirm who is responsible for backing it up. In our experience, ‘we assumed the vendor was backing it up’ is one of the most common gaps we find in this exercise, and it’s rarely true.
Step 3: Build an OT Specific Backup Plan
OT backup differs from IT backup in what needs protecting and how recovery actually works:
- Configuration and firmware, not just data. For controllers and industrial equipment, the critical thing to back up is often the device configuration and firmware version, not a data file. Losing this can mean a full reinstall and reconfiguration from scratch, sometimes requiring the original installer.
- Vendor dependency in recovery. Confirm in advance whether restoring a device requires vendor involvement, licensing reactivation, or specialist knowledge your team doesn’t have in house. This should be documented before an incident, not discovered during one.
- Realistic recovery time objectives. A server can often be restored in hours. Physical OT equipment may need a technician on site, replacement hardware, or a vendor callout, all of which take longer. Your disaster recovery plan should reflect that reality rather than assuming OT recovers as fast as IT.
- Air gapped or offline backups for critical systems. Where an OT system controls something safety critical or business critical (production line, medical equipment, security systems), a backup that’s isolated from the main network reduces the risk of it being encrypted in the same ransomware event as everything else.
Step 4: Build an OT Specific Security Plan
Because many OT devices can’t be patched the way IT systems can, security has to be built around them rather than solely applied to them:
- Network segmentation. OT devices should sit on a separate VLAN from core business IT, with tightly controlled rules for what can talk to what. This limits how far a compromise can spread in either direction.
- Access control. Default credentials on OT devices are one of the most common findings in any security review. Every device should have unique, managed credentials, and remote vendor access should go through a controlled, logged, time limited method rather than a permanent open connection.
- Monitoring. OT devices should feed into the same monitoring and alerting used for the rest of the network, so unusual activity (a device suddenly communicating somewhere new, for example) gets flagged rather than going unnoticed for months.
- A documented patch and lifecycle policy, even if the answer for a given device is ‘cannot be patched, compensating controls are X and Y.’ An explicit, documented decision is very different from an undocumented gap, both for your actual security and for your compliance evidence.
A Practical Starting Checklist
- Physically walk every site and list every OT device, network connected or not
- Run a network scan to catch anything the walkthrough missed
- For each device, confirm what data it produces and where that data is stored
- Confirm, in writing, who is responsible for backing up each data location
- Test restoring at least one OT configuration to confirm the backup actually works
- Segment OT devices onto their own network, separate from core IT
- Replace default credentials and document who holds access to what
- Add OT devices to existing security monitoring
- Document a patch or lifecycle decision for every device, including ‘cannot patch, mitigated by X’
- Review the whole map annually, or whenever new equipment is installed
FAQs
What is the difference between IT and OT?
IT manages data, applications, and communication (email, files, servers). OT manages physical equipment and processes (building systems, industrial controls, medical devices, CCTV). OT is often managed by equipment vendors rather than an IT team, which is why it tends to fall outside standard IT security and backup coverage.
Why does OT need a separate backup plan from IT?
OT backups typically need to capture device configuration and firmware, not just data files, and recovery often depends on vendor involvement or specialist knowledge that takes longer than a standard IT restore. Treating OT recovery time the same as IT recovery time usually leads to unrealistic disaster recovery expectations.
Does OT need to be included in Essential Eight or ISO27001 compliance?
If an OT device is connected to your network or processes business relevant data, it generally falls within the scope of a proper asset inventory and risk assessment under both frameworks. Excluding it because it wasn’t installed by IT is a common but avoidable gap.
How do I find out what OT is connected to my network?
A combination of a physical site walkthrough and a network discovery scan is the most reliable approach. The walkthrough catches offline devices; the scan catches connected devices nobody remembers installing.
Who is responsible for backing up OT system data, us or the vendor?
It depends on the system and needs to be confirmed explicitly rather than assumed. In our experience, businesses frequently assume the vendor is backing up OT data when no such arrangement actually exists.
If you’re not sure what OT is connected to your network, or whether it’s covered by your current backup and security plans, Insource IT can help you map it out and close the gaps. Get in touch.